
Posts
Kubernetes on a Mac, one microVM per pod
Briglet runs the Kubernetes control plane and a node agent as macOS processes on Apple silicon, and boots every pod as its own Linux microVM. This post installs it on a clean Mac, follows a pod into its VM, routes a Service without kube-proxy, and reads the conformance results.
What is an AWS Nitro Sandbox, really?
AWS Nitro Sandboxes give EKS pods, ECS tasks and EC2 workloads hardware-isolated VMs managed by Firecracker without KVM. We examine the architecture, the container and hypervisor escape record, and the reasons Brig uses hvi, a small VMM for macOS and Linux.
How Brig could have interrupted the Binance attack
Binance's initial incident report names the path a malicious interview repository overwrote on an engineer's laptop. That write is a boundary a microVM sandbox can enforce before anyone knows the code is malicious. This post walks through the Brig v0.5.0 setup that contains it: a disposable guest home, no credentials, an egress allowlist, and a credential broker for the agents that do need an API.
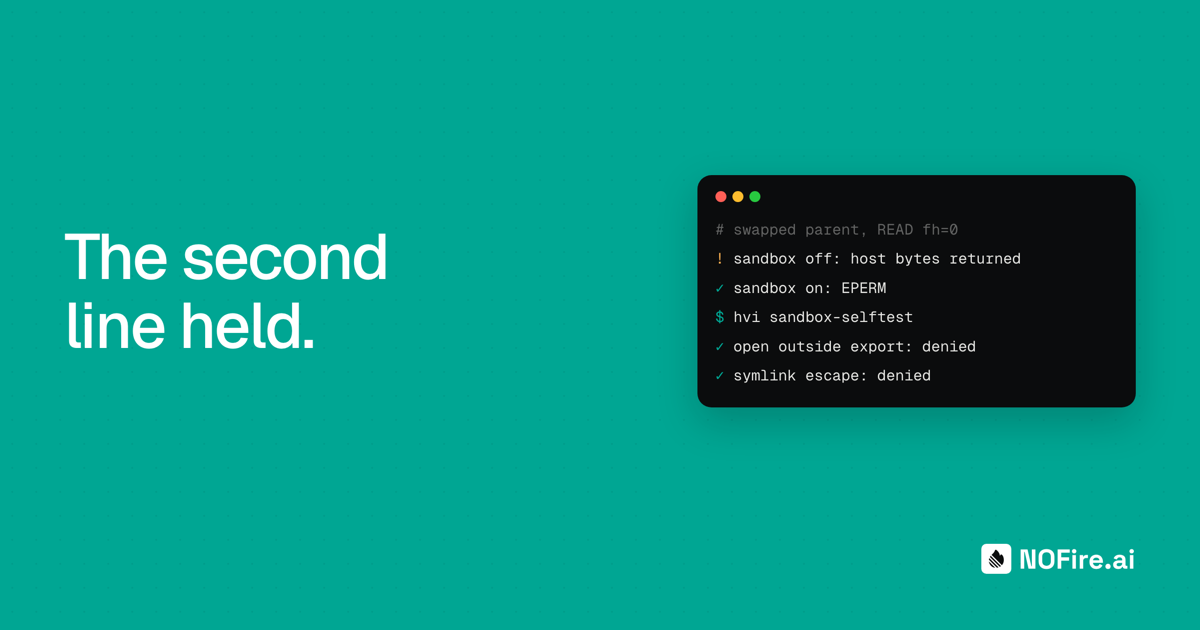
Defense in depth in a microVMM: the virtio-fs path bug our sandbox caught
Docker's macOS VMM lost the host filesystem to a virtio-fs path re-resolution bug (CVE-2026-77179). We replayed the sequence against hvi, our own microVMM. Its handle-based write path held, but one stateless read path exposed the same primitive. The deny-default Seatbelt profile stopped it before the host file could be opened. This post explains the FUSE state involved, the residual exposure, and the descriptor-relative fix.
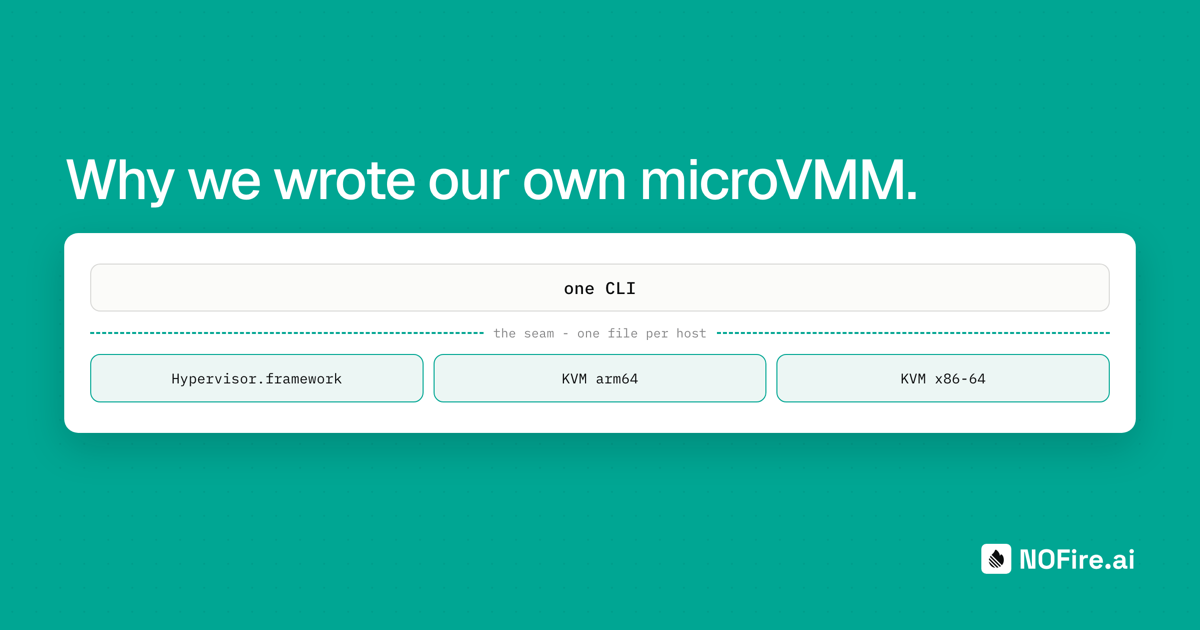
Why we wrote our own microVMM
Our agent sandbox must behave consistently on macOS laptops and Linux servers. Porting Firecracker would require a long-lived fork, so we built a small VMM around an explicit hypervisor interface. This post describes the implementation cost, the components we reused and the work that remains.
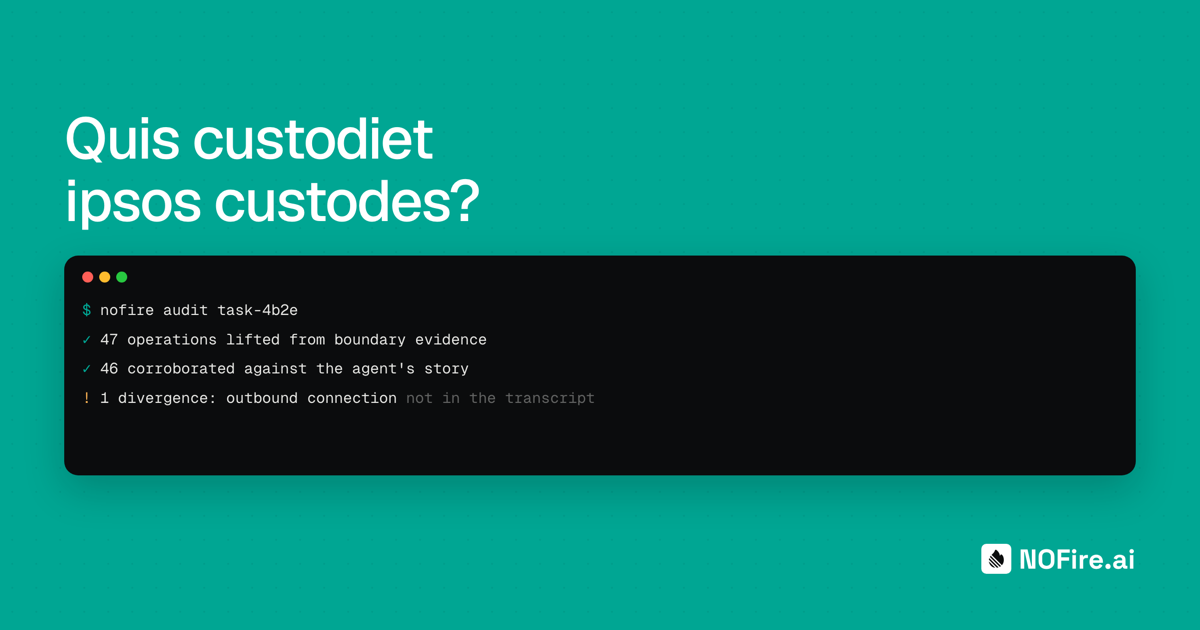
Quis custodiet ipsos custodes?
Every agent platform ships guardrails. Almost nobody asks who watches them. We walk through the trust boundaries of observing an agent from outside its sandbox, why the strongest audit trail is written from a vantage point the agent cannot reach, and how we lift raw boundary events into operations a human can actually read.
The Sandboxing Manifesto
A sandbox is a falsifiable claim. "Sandbox" has been diluted until it guarantees nothing. Ours is a definition sharp enough to be proven wrong: seven checkable properties, enforced by hardware-level microVM isolation, not by configuration.

When the bug is real but the path isn't: ITScape (CVE-2026-46316) and the case for minimal runtimes
ITScape (CVE-2026-46316) is the first public guest-to-host escape on KVM/arm64. We reproduced it on a Jetson AGX Orin and tested which VMMs expose the vulnerable GIC ITS device: all of them except Firecracker up to v1.12.1, with urunc's seccomp filter the only runtime default that blocks it.